Scheduled Task Creation
| Field |
Value |
| ATT&CK technique |
T1053.005 — Scheduled Task/Job: Scheduled Task |
| Tactic |
Execution, Persistence, Privilege Escalation |
| Log source |
Windows Security event log (WS01) |
| Index |
lab_win |
| Severity |
Medium |
| Status |
Validated — 2026-09-24 |
| Author |
Samuel Emerson |
| Created |
2026-09-24 |
| Validated |
2026-09-24 — evidence |
Hypothesis
A scheduled task is one of the most common persistence and privilege-escalation mechanisms on
Windows: it survives reboots, can run as SYSTEM, and looks like ordinary administration. When task
auditing is enabled, Windows writes Security event 4698 when a task is created, recording the task
name and the account that created it. In this environment tasks are not created as part of normal
operation, so any 4698 from an interactive user is worth review.
The event is keyed on creation (4698), not on task update (4701) or task disable (4702), because
both of those already occur in the WS01 baseline from routine Windows servicing and would drown a
detection in noise.
Detection logic
index=lab_win source="XmlWinEventLog:Security" EventCode=4698 NOT SubjectUserName="*$"
| table _time host SubjectUserName TaskName
NOT SubjectUserName="*$" drops tasks created by machine accounts (which end in $), leaving
tasks created by interactive users. A production tuning would allowlist known administration
accounts and scheduled-management tooling.
Field reference
| Field |
Source |
Meaning |
EventCode=4698 |
Security log |
A scheduled task was created |
TaskName |
4698 |
The task path and name, e.g. \spawn |
SubjectUserName |
4698 |
The account that created the task |
EventCode=4699 |
Security log |
A scheduled task was deleted (seen at cleanup) |
Auditing of task creation is off by default; it is enabled here by the STIG audit policy
(Object Access → Other Object Access Events). The detection depends on that setting.
Validation
| Item |
Detail |
| Atomics |
Atomic Red Team master, downloaded 2026-09-24 |
| Test |
#2 Scheduled task Local · 42f53695-ad4a-4546-abb6-7d837f644a71 |
| Command |
SCHTASKS /Create /SC ONCE /TN spawn /TR C:\windows\system32\cmd.exe /ST 20:10 — local tools only, no network |
| Executed at |
2026-09-24 14:45:45 CDT (execution log) |
| Events produced |
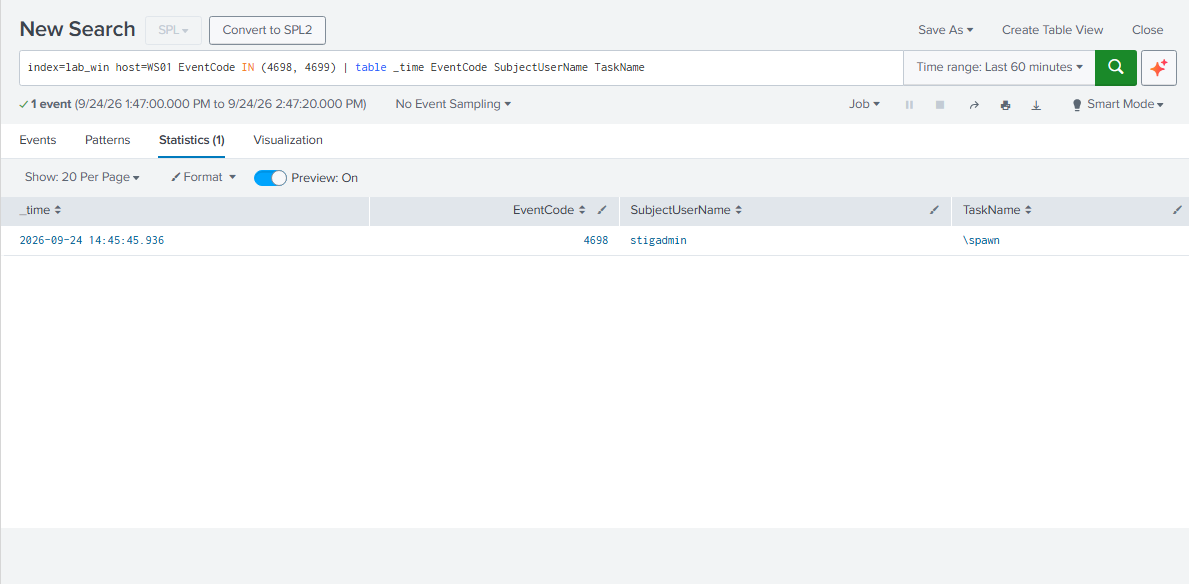
4698, TaskName=\spawn, SubjectUserName=stigadmin |
| Detection fired |
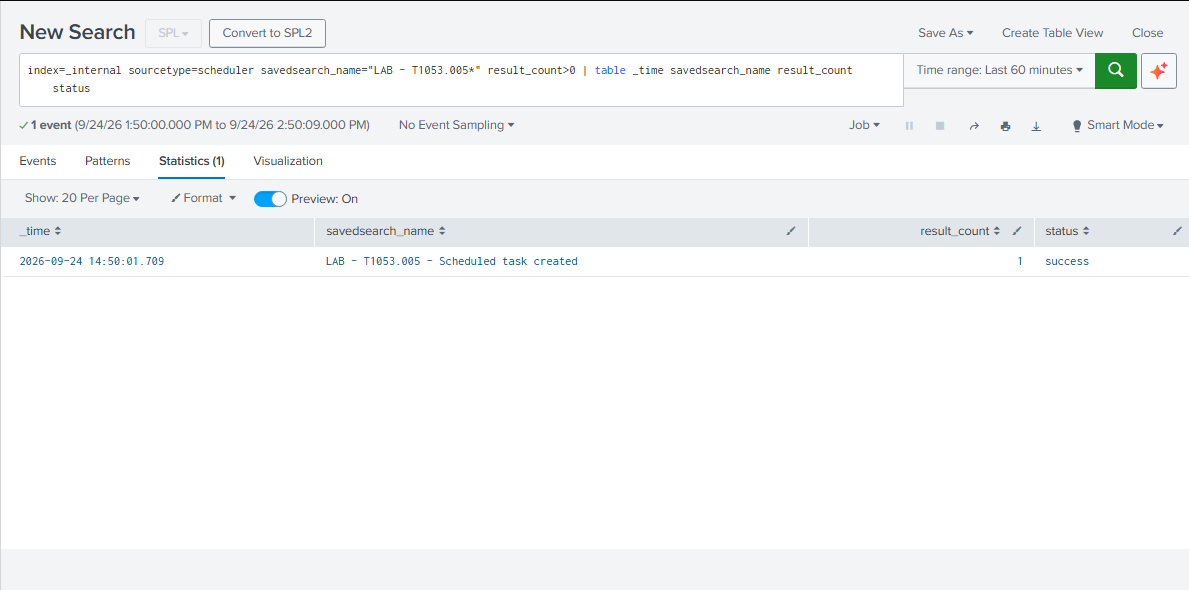
Yes — scheduled run at 14:50:01, 1 result (alert log) |
| Time to detect |
4 min 16 s |
| Evidence |
4698 event · screenshot · alert screenshot |
| Cleanup |
-Cleanup (deletes the task); confirmed with a 4699 in Splunk and schtasks /Query /TN spawn reporting the task was gone |
False positives
| Scenario |
Likelihood |
Tuning |
| Administrator creating a legitimate task |
Medium in production, low in this lab |
Allowlist known admin accounts; alert on tasks whose action is a shell or script interpreter |
| Software installers registering update tasks |
Medium |
Allowlist known publisher task-name patterns after a baseline |
| Management tooling (SCCM, GPO preferences) |
Medium in production |
Allowlist the service accounts those tools use |
Response guidance
- Read the task’s action (the program it runs) and its trigger.
- Identify the creating account and whether it should be creating tasks.
- Check whether the task runs as SYSTEM or another privileged principal.
- Correlate with process creation (4688 / Sysmon 1) at the task’s trigger time.
- If unexplained: disable the task, preserve it for analysis, and pivot to the creating process.
Gaps
- Task creation by directly writing the registry or an XML file under
System32\Tasks — for
example the “Ghost Task” technique (Atomic test #10) — does not always produce a 4698, and would
evade this detection. Pair with a file-integrity or registry monitor on the task store for
coverage.
- Tasks created on the domain controller are out of scope; DC01 does not forward to Splunk.
NIST 800-53 mapping
| Control |
Relevance |
| AU-2 / AU-12 |
Audit of task-creation events |
| CM-6 |
Detecting configuration changes outside the approved process |
| SI-4 |
System monitoring for indicators of unauthorized activity |